InstaWebhook

Blog tag

API security best practices

Articles tagged API security best practices.

By InstaWebhook TeamWebhook Reliability

Zero-Trust Webhook Ingress: Enforcing Cryptographic Sender Identity with DNSSEC, DANE, and Verified mTLS
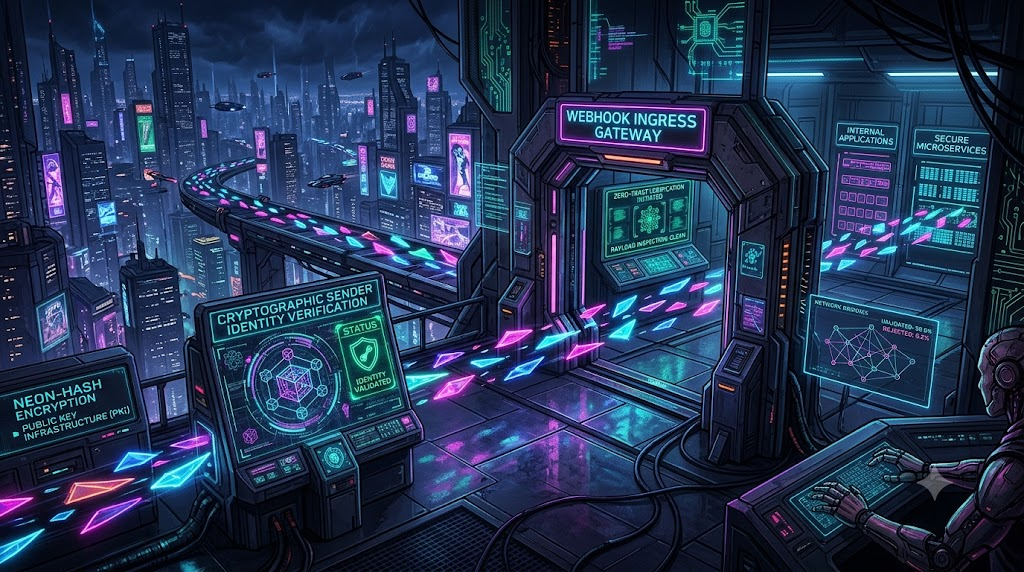
Zero-Trust Webhook Ingress: Enforcing Cryptographic Sender Identity with DNSSEC, DANE, and Verified mTLS

Discover how to secure enterprise webhook infrastructure using DNSSEC, DANE, and edge-level mTLS validation to eliminate static API key vulnerabilities.
By InstaWebhook TeamWebhook Security

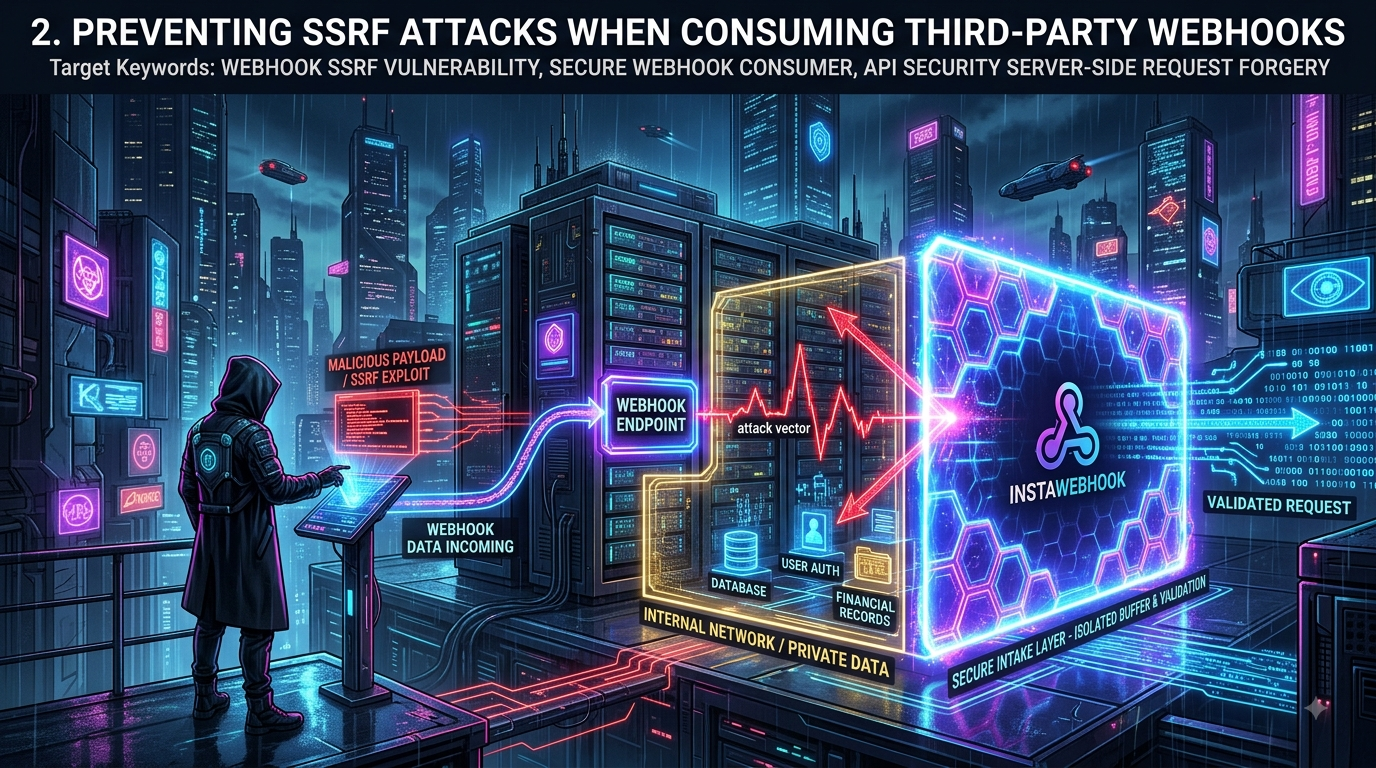
Preventing SSRF Attacks When Consuming Third-Party Webhooks: A Developer's Security Deep Dive

Preventing SSRF Attacks When Consuming Third Party Webhooks A Developer S Security Deep Dive

Preventing SSRF Attacks When Consuming Third-Party Webhooks: A Developer's Security Deep Dive In modern cloud architectures, webhooks are the connective tissue of asynchronous...

By InstaWebhook TeamWebhook Security

The Danger of Exposing Your Main API to Third-Party Webhooks (And How to Fix It)

The Danger Of Exposing Your Main API To Third Party Webhooks And How To Fix It

The Danger of Exposing Your Main API to Third-Party Webhooks (And How to Fix It) As modern web applications become increasingly event-driven, third-party webhooks have become the...

By InstaWebhook TeamWebhook Security

Securing Plaid Webhooks: Best Practices for Financial Data Syncing and Data Sovereignty

Securing Plaid Webhooks Best Practices For Financial Data Syncing And Data Sovereignty

Securing Plaid Webhooks: Best Practices for Financial Data Syncing and Data Sovereignty In modern financial technology, real-time data sync is no longer optional — it's a core...